A record nobody can edit behind your back
Each clock entry stores a SHA-256 hash of its content chained to the previous one. If someone edits the database by hand the chain breaks, and the panel shows exactly which link.
Got a process that lives in a spreadsheet, a WhatsApp group and someone's head? That's exactly the kind of problem I like to solve.
Multi-tenant SaaS for Spanish time-tracking law. Two apps on the App Store and Google Play, tamper-proof audit trail.
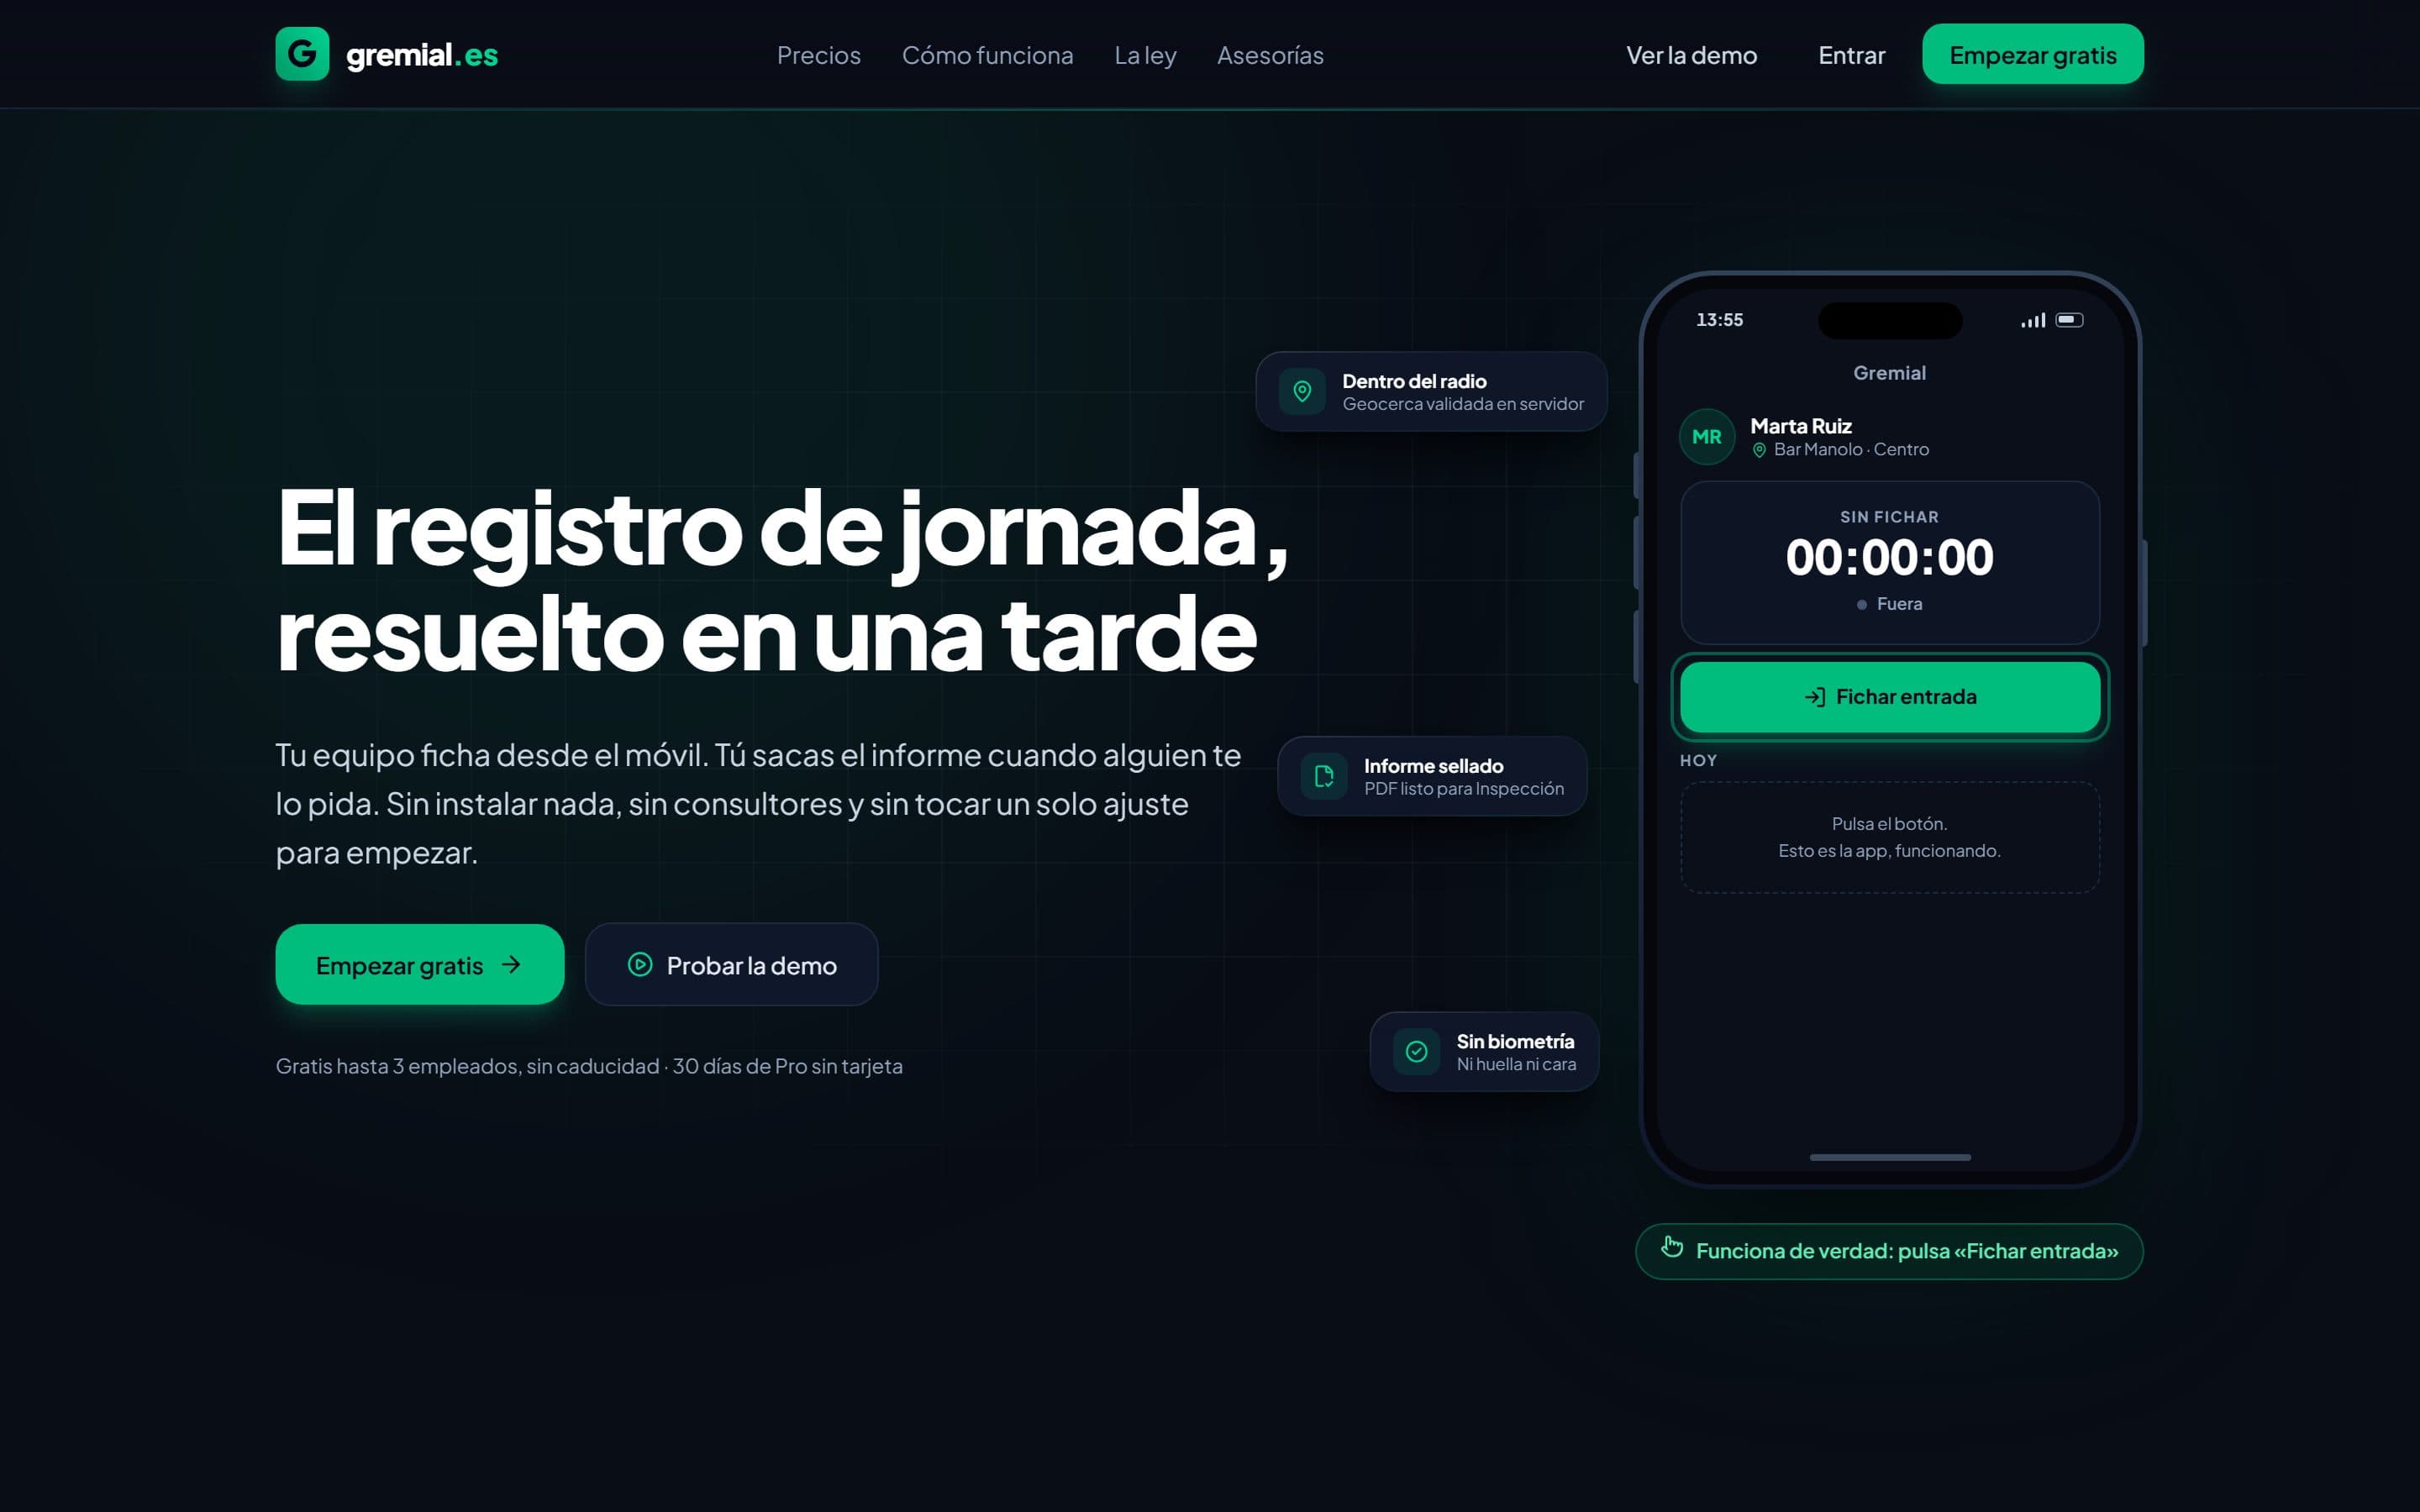
Since 2019 every company in Spain must record each person's working hours and keep them for four years. The bar, the garage or the clinic with 3 to 40 staff is stuck between a spreadsheet that proves nothing and HR suites that need a consultant to roll out. Gremial is built so you sign up and have the team clocking in within ten minutes.
Each clock entry stores a SHA-256 hash of its content chained to the previous one. If someone edits the database by hand the chain breaks, and the panel shows exactly which link.
Editing, creating or voiding an entry is a proposal with a reason that the employee has to accept. It protects the worker, and it's the employer's best defence in an inspection.
No timestamp from the phone is ever trusted. And if the camera, GPS or signal fails, the entry is saved anyway and flagged as having no evidence: complying with the law can't depend on a sensor.
Postgres row-level security, every query through a client bound to the company, and one serializer per audience: no endpoint ever returns a raw row.